

The beautiful tip of the iceberg
Most of what we build you'll never see. This is the part you can.
- Below the surfaceSaaS platforms, cloud systems and the engineering businesses run on.
- Above itA small glimpse of our UI/UX craft — ten real product interfaces.
- Home
- Industries
- Financial services & insurance
Business-critical financial systems, modernised without the drama
From migrating and supporting a major UK insurer's legacy .NET estate to adviser platforms, trusts tooling and AI-driven accounting analytics, we build and run the systems that money and regulation depend on.
Software for financial services & insurance: what we have learned
Financial services software rarely gets replaced in one go. It gets extended, integrated and inherited, until the estate is a mix of a .NET Framework application nobody dares touch, a newer portal, an adviser tool and a dozen integrations with providers, ledgers and regulators. Our job is to make that estate safe to change again.
We have migrated and supported business-critical legacy .NET applications and services for a major UK insurer, built adviser-facing content and search tooling on Blazor and Azure with hybrid DevOps, delivered an online trusts tool for financial services, and designed StratGem-AI, which turns raw accounting data into real-time insight. We also run SendInvoice, our own cloud-native invoicing product, so we live with the same regulatory and uptime expectations as our clients.
Everything ships through pipelines with review, regression tests and a rollback measured in seconds, and everything stays in your name: code, subscriptions, secrets and documentation. That is what lets a compliance team sign off a release and a board sign off a supplier.
How we work with you
- Legacy .NET upgrade & migrationOff end-of-support Windows and SQL Server
- Legacy application supportPatched, monitored, audit-ready
- Development partner transitionStructured takeover from an outgoing supplier
- AI software developmentResponsible AI on financial data
Before you sign anything
What makes financial services & insurance software hard
The problems we are usually called about. If two of these sound familiar, the conversation is worth having.
Legacy platforms reaching end of support
Windows Server 2016 leaves extended support in January 2027 and older SQL Server versions already have. The applications on them still run the business.
Regulation that touches every release
Change control, segregation of duties, audit trails and evidence for FCA, PRA or internal audit have to be part of the delivery pipeline, not a document written afterwards.
Integrations that fail quietly
Provider APIs, payment gateways, accounting packages and data feeds rotate credentials and change versions. The first sign is usually a customer.
Knowledge concentrated in a few people
The engineer who understands the policy engine is retiring or the supplier is winding down, and nobody has written it down.
Our answer, in financial services & insurance
Built on .NET, Blazor and Azure by a UK team with Microsoft-certified engineers, and supported under a written SLA once it is live.
Legacy .NET migration and support
Move .NET Framework, ASP.NET and SQL Server workloads onto supported platforms or Azure, release by release, with parallel running and no big-bang rewrite. Then support them under an SLA.
Adviser and customer platforms
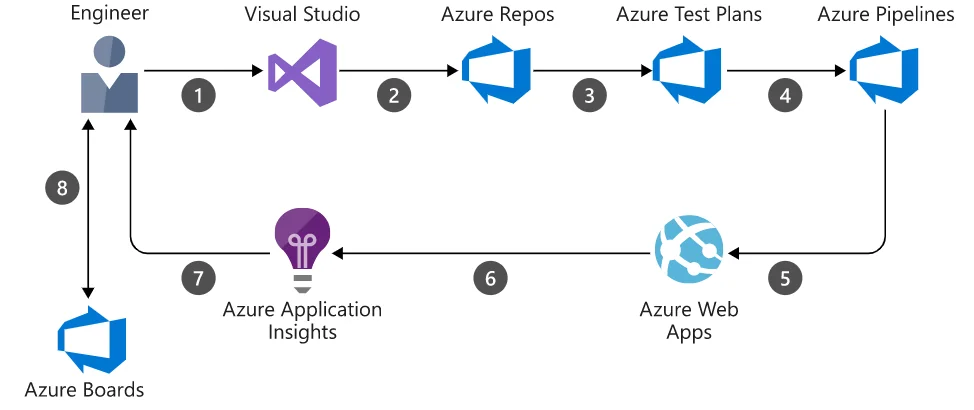
Blazor front ends with Azure Search, secure identity and content management, delivered through Azure DevOps pipelines that satisfy change control.
Analytics and AI on financial data
StratGem-AI turns accounting data into insight in real time. AI reads the data faster than any of us; a named engineer verifies every model and every insight before it becomes an action.
Everything in writing
A published MSA and DPA, Cyber Essentials Plus, severity-based SLAs and a monthly service report your board can read unedited.
Financial services & insurance work we can show you
Systems we have built, taken over and moved forward for organisations like yours. Full write-ups on each page, and reference conversations on request.


Technology we use for financial services & insurance
One Microsoft stack, end to end, so there is one team to call and no hand-off gap in an incident.
Further reading
Security, compliance and continuity
Financial services work is delivered under a published MSA with a UK GDPR Article 28 DPA, Cyber Essentials Plus, segregation between development and security administration, MFA and least privilege on every administrative account, and a change process that leaves an auditable record for every release. Escrow of source code, documentation and runbooks is available for continuity.
Financial services & insurance software: frequently asked questions
Can you migrate our .NET Framework applications without a rewrite?
In most cases, yes. We move applications onto supported Windows Server and SQL Server versions or Azure PaaS release by release, keeping the business logic and running the old and new side by side until the regression suite and your users agree it is safe to switch.
How do you handle change control and audit?
Every change carries a ticket, an approval, a named reviewer and a pipeline run, and that record is retained. Releases go to a staging slot, pass regression and smoke tests, then swap into production with a rollback measured in seconds. Your auditors can read the trail.
What happens if your key engineer is unavailable, or if Assemblysoft ceased trading?
Every account has a lead and a second engineer, and knowledge lives in repositories, runbooks and recorded sessions rather than one head. Source code, documentation and runbooks can be held in independent escrow, and everything is already in your name and defined as code, so anyone you appoint can rebuild it.
Do you work with existing IT, security or audit partners?
Yes. We coordinate with your IT provider, security team and auditors as a matter of course, and we keep development and security administration deliberately separate.
Can we start with a review before committing?
Yes. A maintainability review or discovery assessment is a short, fixed-scope piece of work that ends in a written report, a risk register and costed options. The report is yours whoever you appoint.
Industries we also work in
Talk to us about your financial services estate
Tell us what you run and what keeps you up at night. A short conversation, under NDA if you prefer, is enough to tell you honestly whether we are the right partner and what the first step would cost.
Book an initial discussion Watch how we partnerCyber Essentials Plus · UK-based team · Microsoft Partner · Published rate card and Trust Centre
Start a meaningful conversation with us today.
Assemblysoft are Your Safe Pair of Hands

Azure

Azure DevOps
